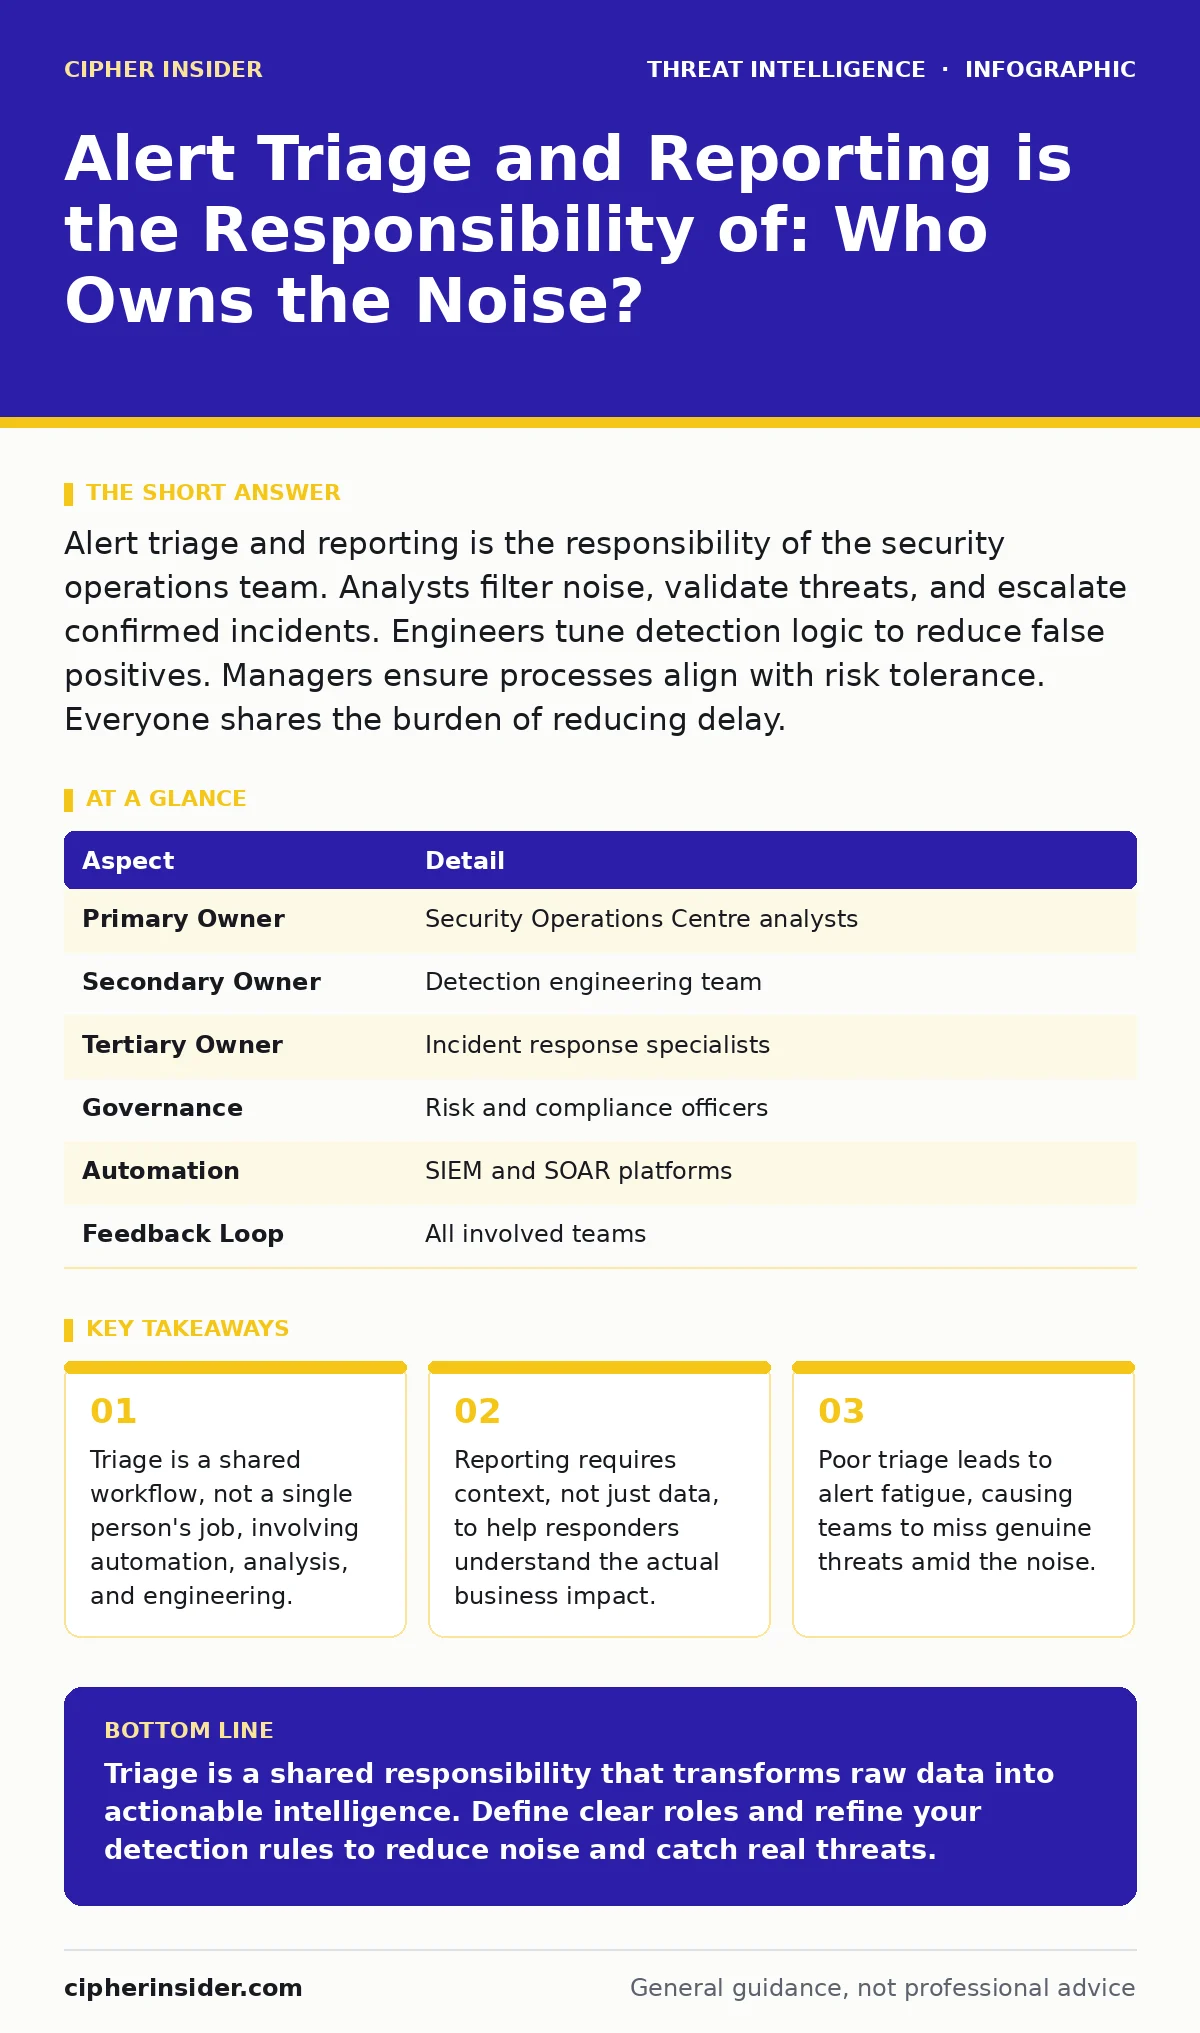
Alert triage and reporting is the responsibility of the security operations team. Analysts filter noise, validate threats, and escalate confirmed incidents. Engineers tune detection logic to reduce false positives. Managers ensure processes align with risk tolerance. Everyone shares the burden of reducing delay.
Understanding the Core Mechanism
Alert triage is the process of sorting incoming security alerts to determine which require immediate attention. Reporting is the act of documenting findings so other teams can act on them. These two functions form the backbone of any security operations centre. Without them, an organisation drowns in data. With them, you turn noise into signal. The goal is not to catch every attack, but to catch the ones that matter before they cause harm.
Imagine a busy airport security checkpoint. Every passenger triggers an alarm for a metal object. Most are keys or coins. A few are weapons. The scanner is the detection tool. The officer who decides which bag to open is the triage agent. The report they write tells the police what to expect. If the officer opens every bag, the line stops moving. If they ignore all alarms, threats pass through. Triage balances speed with accuracy.
Alert Triage and Reporting is the Responsibility of
When you search for "alert triage and reporting is the responsibility of", you are looking for accountability. The answer is rarely a single job title. It is a chain of custody. The security operations centre team owns the initial sort. They decide if an alert is true or false. The vulnerability management team owns the fix. They patch the hole the attacker used. The incident response team owns the containment. They stop the spread. Leadership owns the risk. They decide how much noise is acceptable.
| Aspect | Detail |
|---|---|
| Primary Owner | Security Operations Centre analysts |
| Secondary Owner | Detection engineering team |
| Tertiary Owner | Incident response specialists |
| Governance | Risk and compliance officers |
| Automation | SIEM and SOAR platforms |
| Feedback Loop | All involved teams |
This distribution prevents bottlenecks. If one person does everything, they become the single point of failure. If everyone does something, the system is resilient. You must define who does what before an incident occurs. Ambiguity during a crisis leads to paralysis. Clear roles allow parallel action. The analyst validates. The engineer tunes. The responder contains. Each step depends on the previous one being correct.
How the Workflow Operates
The workflow begins with data ingestion. Your security tools send alerts to a central platform. Most of these alerts are noise. They are false positives. They are low-risk events that do not require action. The first stage is automated filtering. Rules discard obvious junk. A login from a known device at a normal time is ignored. A login from a new country at 3am is kept. This reduces the volume significantly.
The second stage is human review. An analyst looks at the remaining alerts. They check for context. Is the user on holiday? Is the server being patched? They correlate events. One alert might be harmless. Two alerts together might show an attack. They assign a priority. Critical threats get immediate attention. Low-priority items get queued. This step requires judgment. Experience helps, but procedures help more.
The third stage is reporting. The analyst writes a brief. It includes what happened, why it matters, and what to do next. This report goes to the next team. If it is a bug, it goes to engineering. If it is a breach, it goes to response. The report must be clear. Jargon confuses readers. Ambiguity causes delays. A good report tells a story. It connects the dots for someone who did not see the raw data.
What People Usually Get Wrong
Many organisations treat triage as a disposal task. They think the goal is to clear the queue. This is wrong. The goal is to find threats. Clearing the queue is a side effect. If you rush to clear alerts, you miss subtle signs. You might dismiss a slow attack as noise. You might ignore a small breach that grows. Speed without accuracy is dangerous. Accuracy without speed is useless. You need both.
Another mistake is siloed reporting. Analysts report to their managers. They do not report to the teams who need the data. This creates blind spots. The engineering team does not know what to patch. Information stays trapped. It does not flow. You must break down these silos. Reports should go to the people who act on them. Not just the people who watch them.
A third error is ignoring the feedback loop. When an alert turns out to be false, you must fix the rule. If you do not, the noise returns. It builds up over time. The system becomes less effective. You are running on a treadmill. You work hard, but you go nowhere. Triage must improve the detection logic. Every false positive is a chance to learn. Every missed threat is a chance to adjust.
The Role of Automation and Tools
Automation handles the repetitive tasks. It filters obvious noise. It enriches alerts with context. It checks threat intelligence feeds. It correlates events across multiple sources. This frees analysts for complex decisions. They can focus on the hard cases. They can look for patterns that machines miss. Automation does not replace humans. It amplifies them.
Threat intelligence platforms provide external context. They tell you if an IP address is malicious. They show you if a file hash is known bad. This helps analysts make faster decisions. They do not have to look it up. The information is there. They just have to interpret it. This reduces cognitive load. It allows them to focus on the unique aspects of the alert.
Log management is the foundation. You cannot triage what you do not see. You must collect logs from all relevant sources. Servers, networks, applications, identities. If a source is missing, you have a blind spot. The attacker can hide there. Triage depends on completeness. You must ensure your logging strategy covers the critical assets. Gaps in logging lead to gaps in detection.
See also: Detection Engineering: How to Build Signals That Catch Threats · Smart home privacy risks: recovery steps after a sensor leak
Impact on Operations and Staff
Triage affects everyone in the security team. Analysts suffer from alert fatigue if the noise is high. They become desensitised. They miss real threats. They burn out. They leave the job. This creates a staffing crisis. You lose experienced people. You hire replacements. They take time to train. The cycle repeats. You must reduce noise to keep staff.
Engineers suffer from vague requests. If analysts report "something bad happened", engineers do not know what to fix. They must dig for details. This wastes time. It frustrates both sides. Clear reporting solves this. Specific details allow quick fixes. Engineers can patch the right hole. They can tune the right rule. This builds trust between teams.
Management suffers from lack of visibility. If triage is chaotic, leaders do not know the risk. They cannot make informed decisions. They might overinvest in tools. They might underinvest in people. They might ignore real risks. Good triage provides clarity. It shows what is happening. It shows what is working. It shows what needs improvement.
Improving Your Triage Process
Start by defining your metrics. Track time to detect. Track time to respond. Track false positive rate. Track analyst satisfaction. These numbers tell you how well you are doing. They show where you need to improve. Without metrics, you are guessing. With metrics, you are managing.
Next, refine your detection rules. Remove rules that generate constant noise. Add rules that cover blind spots. Use threat intelligence to prioritise. Focus on high-impact assets. Ignore low-impact noise. This reduces the volume. It increases the quality. You see less, but you see better.
Finally, foster collaboration. Hold regular meetings between analysts, engineers, and responders. Share stories. Discuss mistakes. Learn from each other. Build a culture of continuous improvement. Triage is not a one-time fix. It is an ongoing process. You must keep tuning. You must keep learning. You must keep adapting.
Related topics such as NTLM relay attacks require specific detection logic. If you do not have it, you will miss these threats. Honeypots can help validate alerts by attracting attackers. Privilege escalation attacks often start with small anomalies. Hacktivism may look like noise until it scales. LSASS credential theft is a critical event. Attacker persistence techniques hide in plain sight. Log management ensures you have the data to find them. Threat intelligence platforms provide the context to prioritise them. Each of these topics feeds into the triage process. You must understand them to triage them.
Key takeaways
- Triage is a shared workflow, not a single person's job, involving automation, analysis, and engineering.
- Reporting requires context, not just data, to help responders understand the actual business impact.
- Poor triage leads to alert fatigue, causing teams to miss genuine threats amid the noise.
Triage is a shared responsibility that transforms raw data into actionable intelligence. Define clear roles and refine your detection rules to reduce noise and catch real threats.
Frequently asked questions
Who writes the final incident report?
The analyst who validated the alert usually drafts the initial report. The incident response team adds containment details. The engineering team adds remediation steps. Leadership reviews for compliance.
How do I reduce alert fatigue?
Tune your detection rules to filter common false positives. Use automation to enrich alerts with context. Focus on high-impact assets. Train analysts to recognise benign patterns.
What is the difference between triage and response?
Triage is deciding what is real and how urgent it is. Response is acting on that decision to contain and fix the threat. Triage comes first. Response follows.
Can automation replace human analysts?
No. Automation handles volume and routine checks. Humans handle context, ambiguity, and novel threats. You need both for effective security operations.
How this guide was produced: written by the Cipher Insider editorial team with AI assistance, checked against the public references listed below, and reviewed when the facts change. See our editorial policy or report an error.